Is cyber security a good career in India in 2027? Yes. But it works for a narrower set of people than the YouTube thumbnails suggest, and the easy way in is closing.
That is the whole article in two sentences. The rest is evidence, because you should not make a career decision on vibes, mine included.
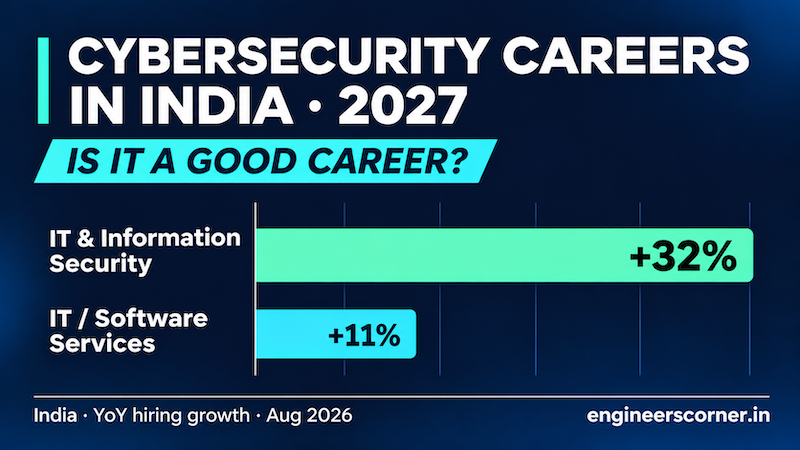
Quick answer: Cybersecurity is a good career in India in 2027 if you are willing to buildreal, hands-on skills before your first job. Demand is rising: IT and information securityhiring was up 32% year on year in August 2026, against 11% for IT overall. But most of thatdemand is for people who can show proof of skill. The traditional fresher route, sitting in aSOC and watching alerts all day, is shrinking as AI takes over first-level triage. The safestbets for 2027 are cloud security, application security, governance and privacy (India’sDPDP rules come fully into force in May 2027) and AI security.
Here is the odd situation as of November 2026. In India, security hiring is growing fasterthan IT as a whole. In the US, cybersecurity job postings just fell to a four-year low. Bothare true at the same time. Why they can both be true is the most useful thing a studentcan understand about this field right now.
I work in security, mostly on the cloud and AI side, so I see this from inside the industryand not from a course brochure. I am also not selling a course. There is no “enrol now”button at the bottom of this page.
What this article covers:
- what the hiring numbers actually say, for India and the US, with sources
- the part course sellers skip: why entry-level jobs are thin and what AI is doing to them
- what the main jobs look like on a normal working day
- salaries, without the brochure numbers
- the skills that will matter in 2027
- a 12-month plan if you are starting from zero
- who should not pick this field at all
Cybersecurity hiring pulse (updated every month)
I refresh this box every month when new hiring data comes out, so bookmark the page if you are tracking the market.
Last updated: 15 November 2026. Next update: first week of December 2026, after Naukri publishes its November report.
| Signal | Latest reading | Period | Source |
|---|---|---|---|
| India: IT and information security hiring | Up 32% year on year | August 2026 (latest month with a security figure I could verify) | Naukri JobSpeak |
| India: all white-collar hiring | Up 14% (index 2,836 vs 2,480) | October 2026, helped by a soft Diwali base last year | Naukri JobSpeak, via Staffing Industry Analysts |
| India: fresher hiring | Up 15% year on year | August 2026 | Naukri JobSpeak |
| India: cyber incidents tracked by CERT-In | 29,44,248 (14,02,809 in 2021) | Calendar year 2025 | MHA reply in Lok Sabha, via ThePrint |
| US: cybersecurity job postings | 235,786, down 26.4% | January to September 2026 | CyberSN, via Infosecurity Magazine |
| US: AI Security Engineer postings | Up 268.3% | January to September 2026 | CyberSN, via SecurityWeek |
| India: DPDP full compliance deadline | 13 May 2027 | Upcoming | Fisher Phillips |
What the hiring numbers actually say:-
Demand in India is real and growing, but it is pulling hardest at the experienced end.
India: up, and for three clear reasons
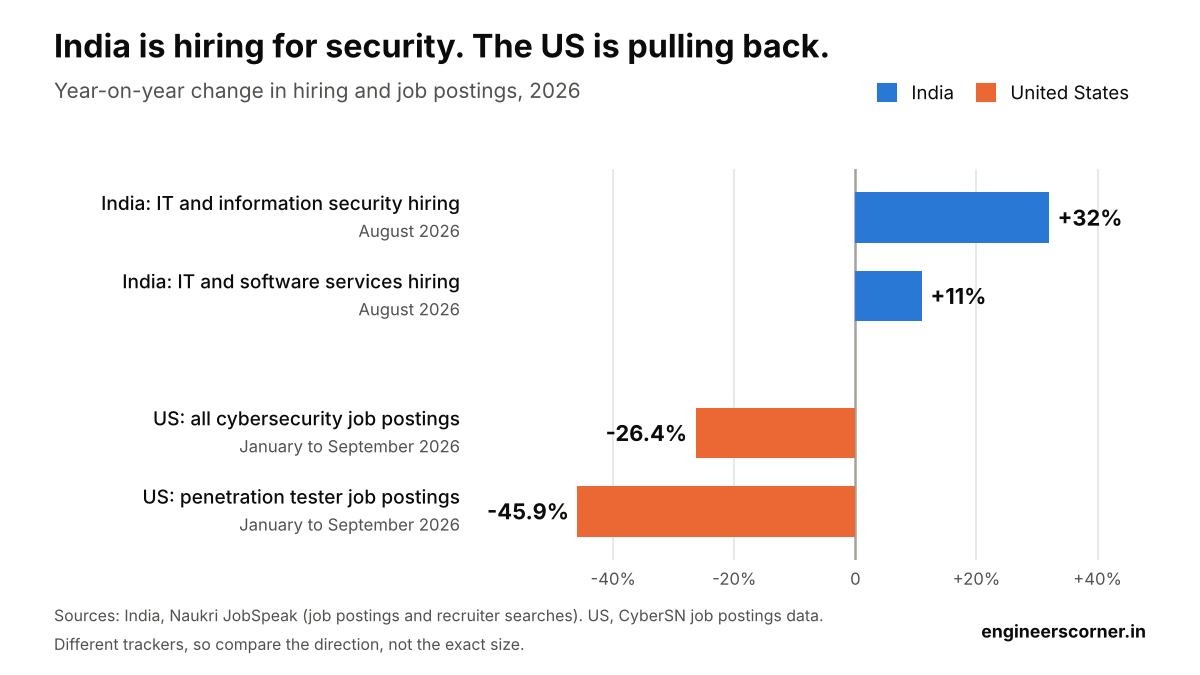
Naukri’s monthly JobSpeak report tracks job postings and recruiter searches on its platform. It put IT and information security hiring up 18% year on year in June 2026, 23% in July and 32% in August. In August, IT as a whole grew only 11%.
The better-paid end moved even faster. In its December 2025 report, Naukri listed security roles paying Rs 20 lakh and above among the standouts: Application Security Engineer up 52%, Manager Information Security up 50%, System Security Engineer up 48% and Security Architect or Consultant up 43%.
Why is India growing when the US is not? Three reasons, and none of them is going away.
- Attacks keep rising. CERT-In tracked 29,44,248 cyber security incidents in 2025, up from 14,02,809 in 2021, according to the Home Ministry’s reply in the Lok Sabha (ThePrint). That is more than double in four years.
- The DPDP deadline. Every company that handles Indian users’ personal data has to be fully compliant with the Digital Personal Data Protection rules by 13 May 2027. Consent, breach reporting, vendor contracts and security controls all need people, and the penalty ceiling is Rs 250 crore.
- It is not just IT companies anymore. TeamLease Digital says cybersecurity hiring is rising across IT services, global capability centres (GCCs), banks, manufacturing and FMCG companies.
The number nobody agrees on
TeamLease estimates that demand for cybersecurity specialists grew 15 to 20% between 2025 and 2026. It says India has around 4 to 5 lakh cybersecurity professionals and nearly 40,000 open positions, with a 25 to 30% shortage at mid and senior levels.
In the same article, staffing firm Xpheno counted slightly more than 7,000 listed cybersecurity openings, broadly stable over two years.
40,000 or 7,000? Both, probably. One number is roughly what companies want to fill. The other is what is actually advertised on a given day. If you are a fresher, the 7,000 is the one that matters for your inbox.
One more detail from Xpheno is worth noticing. Joining ratios have dropped to about 65%, from 75 to 80% earlier. In plain words, people with offers are holding more than one and picking. That only happens when skilled candidates have bargaining power.
The US: a four-year low, with a twist
US cybersecurity job postings fell 26.4% to 235,786 between January and September 2026, the lowest in the four years CyberSN has tracked (Infosecurity Magazine). Before you panic, CyberSN itself says it is not clear whether this means weaker demand or just a return to normal after an unusually strong 2025. Postings across the three 2026 quarters also stayed within 1.5% of each other. Demand has levelled off at a lower point rather than collapsing.
The twist is in what fell and what grew (SecurityWeek):
- Fell: penetration tester down 45.9%, threat hunter down 40%, CISO down 38.9%
- Grew: AI Security Engineer up 268.3%, cyber data scientist up 203.5%
Read that list twice if your plan is “I will do ethical hacking.” The classic pentester role is the one shrinking fastest in the world’s biggest security market.
Why should an Indian student care about US numbers? My read: a lot of Indian security work, in service companies and GCCs, is done for clients and parent companies abroad. What happens there tends to reach here a little later. If you want the wider context, I wrote about the 2026 tech layoffs earlier this year.
The pattern across both countries is the same. Demand is moving towards experienced people and new specialisms, and away from generic roles.
The part course sellers skip
Companies say they cannot find people. Freshers say they cannot find jobs. Both are telling the truth.
The hiring paradox, in numbers
The Data Security Council of India surveyed enterprises and security service providers for its Indian Cyber Security Skilling Landscape 2025-2026 report, published in May 2026. A few findings explain the paradox better than any opinion can:
- 73% of enterprises and 68% of providers say skilled candidates are hard to find
- 84% take between one and six months to fill a cybersecurity role, and only 3% fill one in under a month
- 63% of enterprises say candidates lack hands-on practical skills
- 45% of enterprises say they do not even have lab environments to build those skills internally
So companies are not short of applicants. They are short of applicants who have actually done the work. And many of them have no setup to train you after they hire you, so they want you to arrive ready.
What AI is doing to the first rung
For years, the standard fresher entry was the Tier 1 SOC analyst: watch the alert queue, check whether an alert is real, escalate the serious ones. It is repetitive work, and repetitive work is exactly what AI agents are now good at.
Omar Santos, who works on AI security at Cisco, put it plainly in an eSecurity Planet interview in August 2026: the Tier 1 SOC analyst role is one of the roles being reshaped fastest. Analysts are increasingly expected to oversee and orchestrate AI systems rather than work every alert by hand.
Three more signals point the same way:
- Gartner predicts that by 2028, security operations teams will have 50% more engineers than analysts (BleepingComputer). The people who build and tune the systems will outnumber the people who watch them.
- Cisco’s survey for the AI Workforce Consortium found that 49% of security leaders called hands-on experience with AI agents the hardest skill to find in entry-level candidates. The same report found that 28.5% of cybersecurity job postings in G7 countries between October 2025 and March 2026 asked for AI skills, up from 14.2% a year earlier (DIGIT).
- Entry-level share is thin across Indian tech. One tracker that looked at 18,752 live tech postings in India between late September and late October 2026 found only 4.3% tagged as entry or junior (Careers360). That covers all of tech, not just security, but security is not immune.
My honest read:-
This does not mean L1 SOC jobs vanish in India next year. Plenty of Indian SOCs, especially at managed security providers, still run on people working shifts. But I would not build my whole plan around landing one, and I would not plan to stay in one for long.
The new version of the entry job looks different. Even the vendors selling AI SOC tools describe it this way: you review what the AI agent did on closed alerts and check whether you would have reached the same answer. You own low-risk cases end to end with a senior checking your work. You feed corrections back so the detections get better, which is the road into detection engineering.
The first rung has not disappeared. It has moved up a step, and you now need to arrive already able to climb.
What the jobs look like on a normal day
Cybersecurity is not one job, and “hacker” is not a job title. These are the seven doors most people actually walk through, and how each one looks heading into 2027.
| Role | What a normal day looks like | Realistic way in | 2027 outlook |
|---|---|---|---|
| SOC analyst | Reviewing alerts, checking suspicious logins and malware hits, writing up incidents, often in shifts | Fresher hiring at managed security providers and service companies | Shrinking at Level 1; the job is shifting to reviewing what AI agents did |
| VAPT / penetration tester | Testing web apps, APIs and networks with written permission, then writing the report (the report is half the job) | Security audit and consulting firms; strong web skills matter most | Audit work keeps it alive in India, where CERT-In has empanelled 237 auditing organisations; US postings fell 45.9% |
| Application security / DevSecOps | Reviewing code, adding security scans to CI/CD pipelines, helping developers fix what the scans find | Developers who learn security, or security people who learn to code | Strong; Application Security Engineer topped Naukri’s list of fast-growing Rs 20 lakh+ security roles in December 2025 (up 52%) |
| Cloud security engineer | Fixing over-permissive IAM roles, public storage buckets and open network rules on AWS, Azure or GCP; reviewing new designs | Cloud or DevOps engineers moving sideways | Strong; 58% of enterprises lack people who connect cloud, apps and identity (DSCI) |
| GRC and privacy | Policies, risk assessments, audits, vendor reviews, and now DPDP consent and breach-reporting processes | Freshers who write well; law and commerce graduates with tech interest also get in | Rising into and beyond the May 2027 DPDP deadline |
| AI security engineer | Testing chatbots and AI agents for prompt injection, limiting what agents can touch, reviewing AI vendors | Usually from AppSec or cloud security, plus hands-on work with AI agents | Fastest growing title: 78% of organisations report high demand (DSCI); US postings up 268% |
| OT / ICS security | Securing factory, power plant and utility systems where downtime is not an option | Electrical, electronics and instrumentation engineers who learn security | Niche and hard to hire: 41% of providers struggle to find people (DSCI) |
Two things in this table deserve a second look.
First, if you are in mechanical, electrical or ECE and think cybersecurity is only for CSE students, look hard at OT security and GRC. Almost nobody tells core-branch students these doors exist, and the OT one in particular is short of people.
Second, the roles with the strongest outlook (AppSec, cloud security, AI security) are not entry-level jobs in the usual sense. People reach them from a neighbouring job. That is not bad news. It just means your first job does not have to have “security” in the title. A developer or cloud engineer who takes security seriously is often closer to these roles than a fresher with a certificate.
If i have to start with zero and with some cloud knowledge i will start with cloud security first and later move to AI security because this makes things more interesting and it also reflects the latest ongoing technology and risk we have nowadays which can cover my role and this is going to be solid protfolio for you and your knowledge in security.
Cybersecurity salary in India, without the brochure numbers
Cybersecurity pays well at the top and ordinary at the bottom, and what separates the two is skill more than years.
| Stage | What the data says | Source |
|---|---|---|
| Fresher (0 to 2 years) | Entry-level pay in AI, cloud and cybersecurity of around Rs 6 to 8 lakh a year; relevant security skills add a 10 to 20% premium in campus placements | TeamLease Digital, 2025 primer and 2026 update |
| Mid-level engineer | Wage premiums of 20 to 22%; cybersecurity salaries overall rose about 20% year on year | TeamLease Digital and Xpheno, 2026 |
| Experienced, at a GCC | Average projected to reach Rs 33.5 lakh by FY27 (April 2026 to March 2027); senior specialists up to Rs 55 lakh | TeamLease Digital, 2025 primer |
| Architect, 15+ years | Cloud security architect at a GCC: estimated median fixed pay of about Rs 98.6 lakh | TeamLease Digital, 2026 |
Yes, that last row is nearly a crore. No, it is not what your first offer will look like. Those are architects with 15 to 20 years behind them, and there are not many of them.
A fair warning about the fresher row. These are averages from a staffing firm’s data, and that data leans towards GCCs and specialised roles. A generic Level 1 SOC offer at a large service company can come in lower. Before you accept anything, look up that exact role at that exact company on AmbitionBox or Glassdoor, and compare in-hand pay, not CTC.
The other thing nobody puts in the brochure: most big jumps in this field come from switching jobs, not from appraisals. In the DSCI survey, 70% of service providers and 42% of enterprises said they lose people mainly because those people move elsewhere for higher salaries. Skills you can prove are what make that move possible.
Skills that will matter in 2027
The fundamentals have not changed. What has changed is that employers now want them combined with cloud and AI.
The boring base (do not skip it)
- Networking: TCP/IP, DNS, HTTP, and what actually happens when you type a URL and press enter
- Operating systems: Linux, and Windows with Active Directory, because so many real breaches still go through stolen or misused identities
- One scripting language: Python is enough, as long as you can automate a boring task with it
- Reading logs: lots of them
AI tools can explain a log line to you. They cannot give you the instinct that a log line looks wrong. That instinct only comes from reading thousands of them, and it is the thing interviewers are quietly testing for.
The 2027 layer:-
1. Cloud security. Pick one cloud (AWS or Azure is fine) and learn identity and access management, logging and the common misconfigurations properly. The DSCI survey found 58% of enterprises and 60% of providers lack people who can connect cloud, applications and identity systems. That combination is where a lot of the hiring pain sits.
2. Application security. Learn the OWASP Top 10, learn to read code you did not write, and learn how security scans fit into a CI/CD pipeline. Developers who understand security are rare and valued.
3. AI security. This is the newest and the most short-staffed area. In the DSCI survey, 83% of organisations called AI and GenAI security skills a critical requirement, and AI/ML security specialists were the hardest talent of all to recruit. In practice it means understanding prompt injection, limiting what an AI agent can access, and checking what an agent does with the tools and data you give it.
This is not theory anymore. In April 2026, researchers showed that a single crafted pull request title or GitHub comment could hijack AI coding agents from Anthropic, Google and GitHub running inside CI pipelines and make them leak secrets (SecurityWeek). Someone has to find and fix that class of problem, and there are very few people who can. For a wider view of where frontier AI is heading, see my post on why the big AI labs suddenly agree on slowing down.
4. DPDP and GRC literacy. Even if you want a technical role, know what India’s data protection rules ask for: consent, breach notification, retention and vendor obligations. With the May 2027 deadline close, engineers who understand compliance get pulled into a lot of rooms.
5. Writing. Every security job ends in a document: a pentest report, an incident summary, a risk note for a manager who has two minutes. If you can explain a technical problem clearly in five lines, you are already ahead of many candidates. This blog post is, in a way, me practising the same skill.
A 12-month cybersecurity roadmap if I were starting from zero
If I were in my second or third year of engineering today, this is the order I would follow. Most of it costs nothing except time.
- Months 1 to 3: build the base.
- Use Linux every day, and work through OverTheWire’s Bandit levels (free)
- Capture your own home network traffic in Wireshark and figure out what each packet is doing
- Learn enough Python to automate one boring task you actually have
- Do the free beginner rooms on TryHackMe
- Keep notes in public, on GitHub or a simple blog. You will need them later
- Months 4 to 6: pick one lane and go deep.
- Web and AppSec: PortSwigger’s Web Security Academy, whose labs are free and better than most paid courses
- Cloud: open a free account on one cloud, misconfigure things on purpose, then find and fix them
- SOC and detection: set up a home lab with a free SIEM such as Wazuh, send it logs from a couple of virtual machines, and write your own detection rules
- AI security: build a small AI agent with a couple of tools, then try to break it with prompt injection. The OWASP Top 10 for LLM Applications is the map
- GRC and privacy: read a good summary of the DPDP rules and write a mock privacy policy and breach-response plan for an imaginary startup
- Months 7 to 9: build proof.
- Finish three projects in your lane, each with a proper write-up of what you did, what broke and what you learnt
- Play CTFs: picoCTF to start, then join a team through CTFtime
- Try bug bounty only on programmes that explicitly invite testing. Never test a website or app without written permission. Unauthorised access is a criminal offence under India’s IT Act, and “I was learning” is not a defence
- Months 10 to 12: certify (maybe) and apply smartly.
- Take one entry-level certification only if your budget allows. It helps you clear HR filters; your write-ups are what get you through the interview
- Apply beyond the obvious names: security audit firms, managed security providers, GCC internships, and non-security first jobs in development, cloud or IT support that you can grow out of
- Be ready to walk an interviewer through every project line by line. That conversation is the real test
Two things most guides get wrong right now:-
The ISC2 CC exam is no longer free. From 2022 until this year, ISC2’s Certified in Cybersecurity was the go-to free first certification, and many blogs still say it is. ISC2 stopped accepting new participants in its One Million Certified in Cybersecurity programme on 20 May 2026 (ISC2). New candidates now pay US $199 for the exam, plus a US $50 annual maintenance fee after passing. If you already have an unexpired free exam code, you must sit the exam by 31 December 2026.
Your job search is an attack surface. The record $6.3 billion theft from crypto exchange Binance in 2026 involved a fake recruiter and a “programming task” that hid malware (GovInfoSecurity). Students get the same kind of “take-home coding assignment” on LinkedIn and WhatsApp every placement season. Run any assignment from an unknown recruiter inside a throwaway virtual machine, read its install scripts before running anything, and be suspicious of a recruiter who rushes you off the job platform. If you want to work in security, this is a good place to start practising it.
Who should not pick cybersecurity:-
This field is a bad fit for some people, and it is kinder to say so now than after two years and a course fee.
Skip it if:
- You want to stop studying after college. Tools and attacks change every year. In G7 countries, the share of security job postings asking for AI skills roughly doubled in a single year. If weekend learning sounds like punishment, this job will feel like one.
- You mainly like the hacker image. Most of the work is reading, checking, documenting and convincing people. Offensive roles are a small slice of the field, and in the US they are shrinking fast.
- You hate writing and meetings. You will write reports and explain risk to people who would rather not hear about it.
- You do not handle pressure at odd hours well. Incidents do not respect weekends or Diwali. Many roles come with shifts or on-call duty.
- You want a guarantee. No degree, certificate or course guarantees a job here. Anyone promising guaranteed cybersecurity placement for a fee is selling the promise, not the job.
It suits people who are curious, patient, enjoy puzzles, and are comfortable being the one in the room who says “wait, this is not safe.”
My honest verdict:-
Is cybersecurity a good career in India in 2027? For the right person, yes, and probably one of the better bets in tech right now. Demand in India is growing, the DPDP deadline guarantees years of compliance and security work, AI has created a brand new specialism that almost nobody is trained for yet, and pay at the experienced end is excellent.
But the easy route for a fresher with a certificate and no proof is over. The jobs are going to people who can show what they have built and broken, and who understand cloud and AI on top of the basics.
If that sounds like work you would enjoy anyway, start this week. Twelve months from now you will be in a very different place from someone who only read articles like this one.
My final take: whatever technical role you pick, security is already part of your job. Developer, tester, cloud architect, DevOps engineer, SRE, even product manager, every one of these roles deals with security from day one, and no one can deny that. Over a career, all of them keep running into security topics again and again, whether it is secure code, access, data or audits.
So if security makes you even a little bit curious, and you enjoy talking about it, why not make it your actual role? Every organisation needs it, and you get to be the person who helps them stay safe and lower their risk.
Also remember that cyber security is just one name. Inside it is a very wide field, with a lot of roles, technologies, tools and skill sets. One person cannot know all of it. Every area goes deep, so you build real expertise in one, maybe a few over time. That is exactly why there are so many opportunities here. And as AI and ML keep growing, so will the threat actors and hackers who use them. This field will keep growing with them, and you have to be ready for it.
Let me know what you think in the comments below.
Frequently asked questions:-
Is cybersecurity a good career for freshers in India?
Yes, if you build hands-on proof before you apply. Entry-level openings are thin, and 63% of Indian enterprises in the DSCI survey said candidates lack practical skills. Freshers with labs, projects and write-ups stand out quickly because so few have them.
Will AI replace cybersecurity jobs?
AI is replacing tasks, not the field. Repetitive Level 1 SOC triage is being automated fastest, and Gartner expects security operations teams to have 50% more engineers than analysts by 2028. At the same time, AI Security Engineer postings in the US rose 268.3% in the first nine months of 2026.
What is the salary of a cybersecurity fresher in India?
TeamLease Digital puts entry-level pay in AI, cloud and cybersecurity at around Rs 6 to 8 lakh a year. Generic Level 1 SOC offers at large service companies can be lower, so check the exact role and company on AmbitionBox or Glassdoor and compare in-hand pay, not CTC.
Can I get into cybersecurity without coding?
Yes. Governance, risk, compliance and privacy roles need clear writing and an understanding of laws like the DPDP rules more than code. That said, basic Python helps in almost every security role, including SOC work.
Is the ISC2 CC exam still free?
No, not for new candidates. ISC2 closed its free One Million Certified in Cybersecurity programme to new participants on 20 May 2026. The exam now costs US $199, plus a US $50 annual maintenance fee after passing, and existing free codes must be used by 31 December 2026.
Is B.Tech CSE (Cyber Security) worth it?
It is worth it if the college has real labs, a CTF culture and faculty who actually practise security. If the specialisation is a regular CSE syllabus with a few extra theory papers, a normal CSE degree plus your own projects will take you just as far.
Cybersecurity or AI/ML: which is better in 2027?
You do not have to choose. In August 2026, Naukri recorded AI/ML hiring up 31% and IT and information security hiring up 32%. AI security sits exactly between the two, and it is the most short-staffed area in Indian security right now.
Which cybersecurity roles are hardest to hire for in India?
In the DSCI survey, security architects topped the list (49% of providers and 40% of enterprises struggle to hire them), followed by OT and industrial control system specialists and advanced threat intelligence professionals. AI and ML security specialists were the most constrained talent area overall.